A Georgetown clinic introduces online appointments. Patients enter their names, telephone numbers and a short description of why they want to see a doctor. The new form reduces waiting time, but it also creates questions the clinic never had to answer when bookings were written in one book behind the reception desk.
Who can see the information? Does the software company hosting the form receive a copy? How long should the clinic keep an abandoned booking? If a receptionist downloads the appointment list to a personal laptop, which controls still apply? And if the wrong patient receives an email containing someone else's details, who takes responsibility?
These are data-protection questions, but they are also ordinary management questions. Every business that employs people, accepts payments, keeps customer records or uses cloud software handles information about individuals. Understanding data protection begins with seeing that information as something the business must manage throughout its life—not simply something stored on a computer.
Personal information follows the person, not the format
Personal data is information connected to an identifiable individual. A name or identification number is an obvious example, but the idea is broader. A telephone number, delivery address, employee record, customer account, photograph or online identifier may also point to a person. Information can remain personal even when it sits in a spreadsheet, email, paper file, messaging application or archived backup.
Context matters. A hotel reservation may reveal travel dates and companions. A payroll file may contain bank details and statutory deductions. A contractor's recruitment folder may include identification documents, qualifications and medical information. A retailer's delivery list may appear routine, yet it still connects names with addresses and purchasing activity.
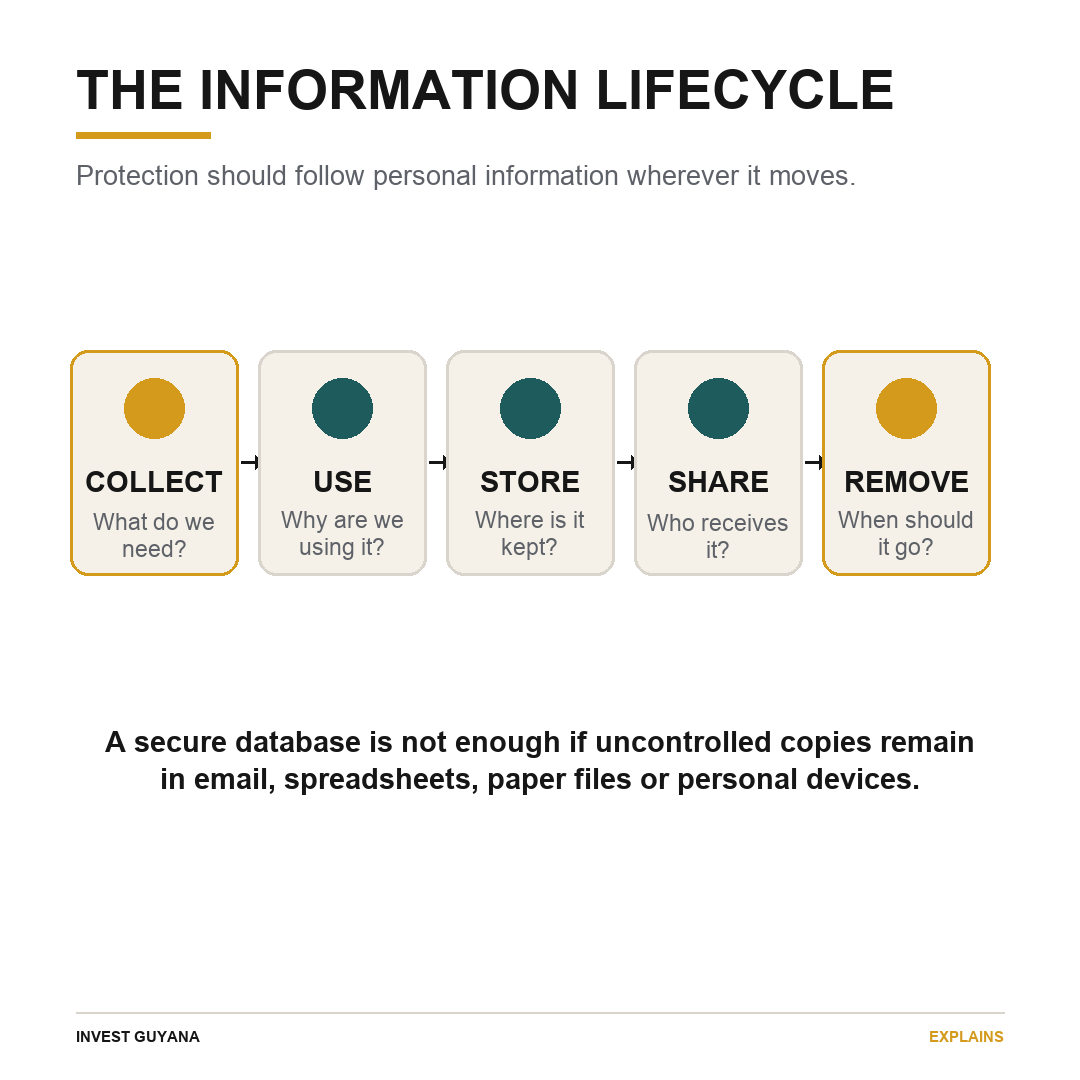
The practical lesson is that protection should follow the information wherever it moves. Locking the main database does not solve the problem if staff routinely export customer lists to shared inboxes or personal devices. A business needs to understand the whole route: collection, use, storage, sharing, archiving and deletion.
Purpose is the first control
The most useful question is often the simplest: why are we collecting this?
If the clinic needs a name and contact number to confirm an appointment, those fields have a clear operational purpose. Asking a patient to describe symptoms in an unsecured booking form may create risk before a clinician needs the information. If a hotel collects an identity document for a lawful check, that does not automatically mean every employee should retain a copy indefinitely.
Purpose disciplines the rest of the system. It helps a business decide what to collect, who should use it, how long it may be needed and when it should be removed. It also exposes “function creep”—the gradual use of information for reasons that were never explained when it was collected. A customer list assembled to deliver orders should not quietly become an unrestricted marketing database without considering whether that new use is appropriate.
Collecting less information can be one of the strongest safeguards. It reduces the material available to be lost, misused or exposed and makes the remaining records easier to control. Data protection is therefore not a demand to keep more paperwork. Done well, it can lead to simpler forms, fewer duplicates and clearer business processes.
Guyana's legal position must be described carefully
Guyana enacted the Data Protection Act 2023. The Act is designed to regulate the collection, keeping, processing, use and dissemination of personal data. It addresses concepts including lawful and transparent processing, defined purposes, accuracy, security, data controllers, data processors and the rights of individuals.
However, enactment and commencement are not the same. Section 1 states that the Act comes into operation on a day appointed by ministerial order and allows different provisions to begin on different days. A search of the Official Gazette undertaken for this article on 5 October 2026 did not identify a commencement order for the Data Protection Act. That means this article does not present every provision of the Act as a currently operative duty.
The position should not be inferred from a title or a separate digital programme. Government reporting in 2026 referred to a Data Protection Commissioner in connection with the national electronic identification system, while also stating that the separate Digital Identity Card Act came into force on 31 March 2026. The commencement of one law, or the existence of an official role, does not by itself establish that every provision of another Act is operative.
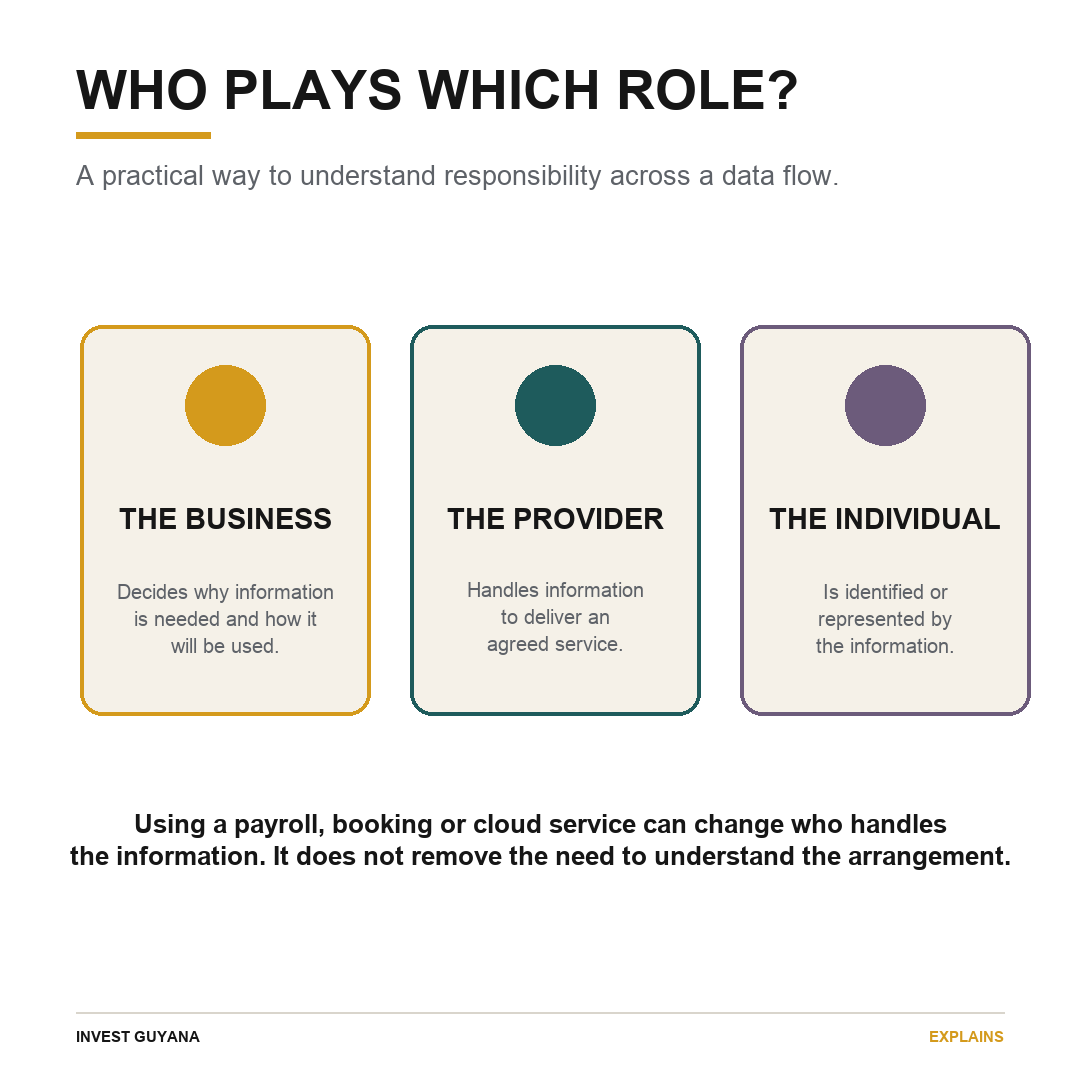
Businesses should verify the latest Gazette position and obtain Guyana legal advice before relying on a particular statutory deadline, registration requirement, exemption or enforcement power. At the same time, the principles described by the Act remain useful for managing information responsibly. The government's own explanation of the legislation emphasised defined purposes, accuracy, security and the distinction between the organisation that decides how data is used and a provider that processes it on that organisation's behalf.
Responsibility does not disappear when a vendor is involved
Many companies do not operate their own servers. They use payroll platforms, booking systems, accountants, cloud storage, payment processors and marketing tools. Outsourcing the technology may improve security and efficiency, but it does not eliminate the need to understand the arrangement.
Before sending personal information to a provider, a business should know what information the provider receives, what service it performs, where the records are held if that is relevant, who may access them and what happens when the contract ends. It should also know who will make contact if the provider suffers an incident.
This matters particularly to international investors. A group company may use a regional human-resources platform or send Guyana customer information to a headquarters system overseas. A privacy policy written for another jurisdiction may not describe the actual flow through the Guyana operation. The local office should map what happens in practice rather than assume that a global document has answered every question.
The same principle applies to small firms. Giving an accountant access to payroll records or uploading customer contacts into a free marketing tool is still a transfer of information to another party. The scale is different, but the management question is the same: what is being shared, for what purpose and under whose control?
Access should reflect the job, not convenience
In many incidents, the problem is not a sophisticated external attack. It is an old account that was never closed, a shared password, a spreadsheet sent to the wrong group or an employee who can view records unrelated to their work.
Access should therefore follow roles. A reservations clerk may need guest contact details but not the entire payroll folder. A supervisor may need staff schedules but not bank information. Someone who changes jobs may require different access, and someone who leaves should lose access promptly across email, cloud storage, business software and physical files.
Good controls also create accountability. Individual accounts, strong authentication and reliable logs help a business understand who performed an action. Shared accounts make investigation difficult and allow poor practices to survive because responsibility is blurred.
Technology is only part of the answer. Staff must know where authorised records belong, how to report a mistake and why sending a file to a personal account creates risk. A system can have sophisticated security while daily work routes around it.
Retention should be a decision, not an accident
Businesses often keep records because deleting them feels risky. Over time, old applications, customer exports, copies of identification documents and former-employee accounts accumulate across several systems.
Some information must be retained for tax, employment, contractual or other legitimate reasons. The correct period may depend on the record and the law governing it. The answer is not one universal deletion date. It is a documented decision that links each category of information to a business or legal reason, identifies where copies exist and explains how disposal will occur.
Keeping everything forever can make the business less secure. Old information increases the volume exposed in an incident and makes it harder to answer a basic question: what do we actually hold about this person? A clear retention process improves both protection and operational discipline.
Accuracy belongs in the same conversation. An outdated address, duplicate employee profile or wrong account status can lead to poor decisions even if no outsider ever sees the record. Businesses should provide a route for correcting material information and prevent unnecessary copies from drifting apart.
When something goes wrong, speed and clarity matter
Return to the clinic. A staff member sends the day's appointment list to the wrong email address. The mistake cannot be undone by pretending it did not happen. The clinic needs a clear reporting route, someone authorised to lead the response and a record of what was sent, to whom and when.
The immediate priorities are to contain further disclosure where possible, preserve evidence, establish which individuals and information are affected, involve the relevant provider and seek appropriate legal or technical advice. Whether a formal notification is legally required will depend on the applicable framework and the facts; it should not be guessed by the employee who made the mistake.
Preparation changes the outcome. If staff know whom to contact, vendor details are available and decision-makers can locate the affected records, the business can respond deliberately. Without that groundwork, valuable time is lost establishing basic facts.
Data protection is part of investment readiness
For investors, information governance affects more than regulatory exposure. A buyer conducting due diligence may want to know whether customer records were collected and managed consistently. A lender or strategic partner may examine cyber controls. A multinational client may require suppliers to meet contractual privacy and security standards. Weak records can complicate integration, reduce confidence and increase the cost of a transaction.
Smaller businesses feel the same issue through trust. A hotel guest expects a booking to remain private. An employee expects payroll details to be controlled. A customer expects an identification document sent for one purpose not to circulate indefinitely. These expectations exist whether or not a dispute reaches a regulator or court.
The clinic in our opening example does not need to begin with a perfect compliance programme. It needs to begin with an honest map of the information it collects, a clear reason for each item, access based on real roles and a response plan that staff can use. Those foundations make legal compliance easier to implement when obligations are confirmed, but they also improve the business today.
The companion Invest Guyana Guide, How to Build a Business Data-Protection Checklist, turns these principles into a practical 30-day workflow. The central idea is straightforward: know what information you hold, understand why you hold it and remain in control of it throughout its life.
Editorial note: This article provides general business information, not legal advice. The commencement position and any applicable requirements should be verified against the latest Official Gazette and professional advice before a business acts on a specific provision.